How to set up the AWS connection
Last updated: October 19, 2026
This guide explains how to connect your AWS environment to Strike to start discovering and monitoring your cloud assets. To learn what Strike Cloud offers and how it is activated, see Strike Cloud: visibility and security over your cloud surface.
Prerequisites
Before you start, make sure you have:
Strike Cloud activated in your organization.
Access to your AWS account with IAM permissions to create roles.
Your organization's cloud account details.
Connect your AWS account
Strike uses a read-only IAM role to access your cloud environment. No permanent credentials are required.
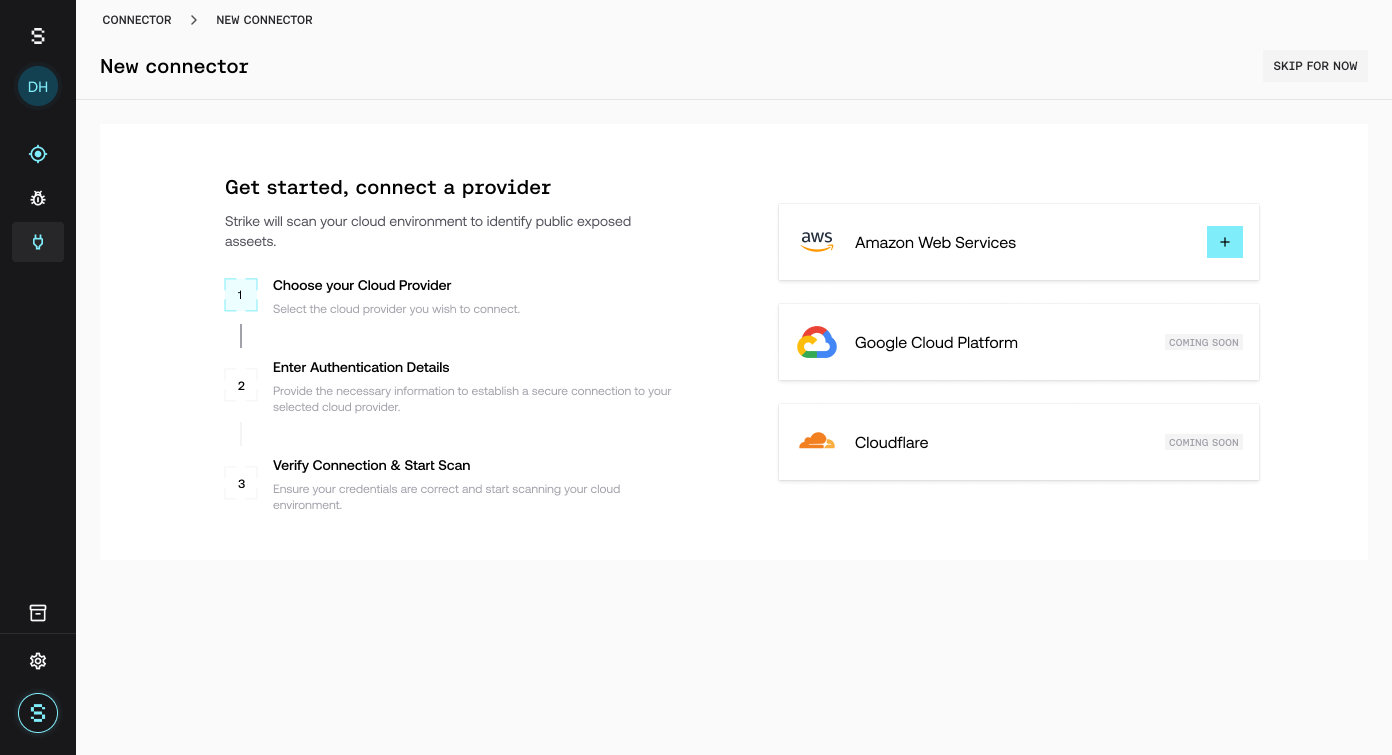
Step 1: Select a cloud provider
Go to Connectors.
Select Amazon Web Services.
Step 2: Name your connector
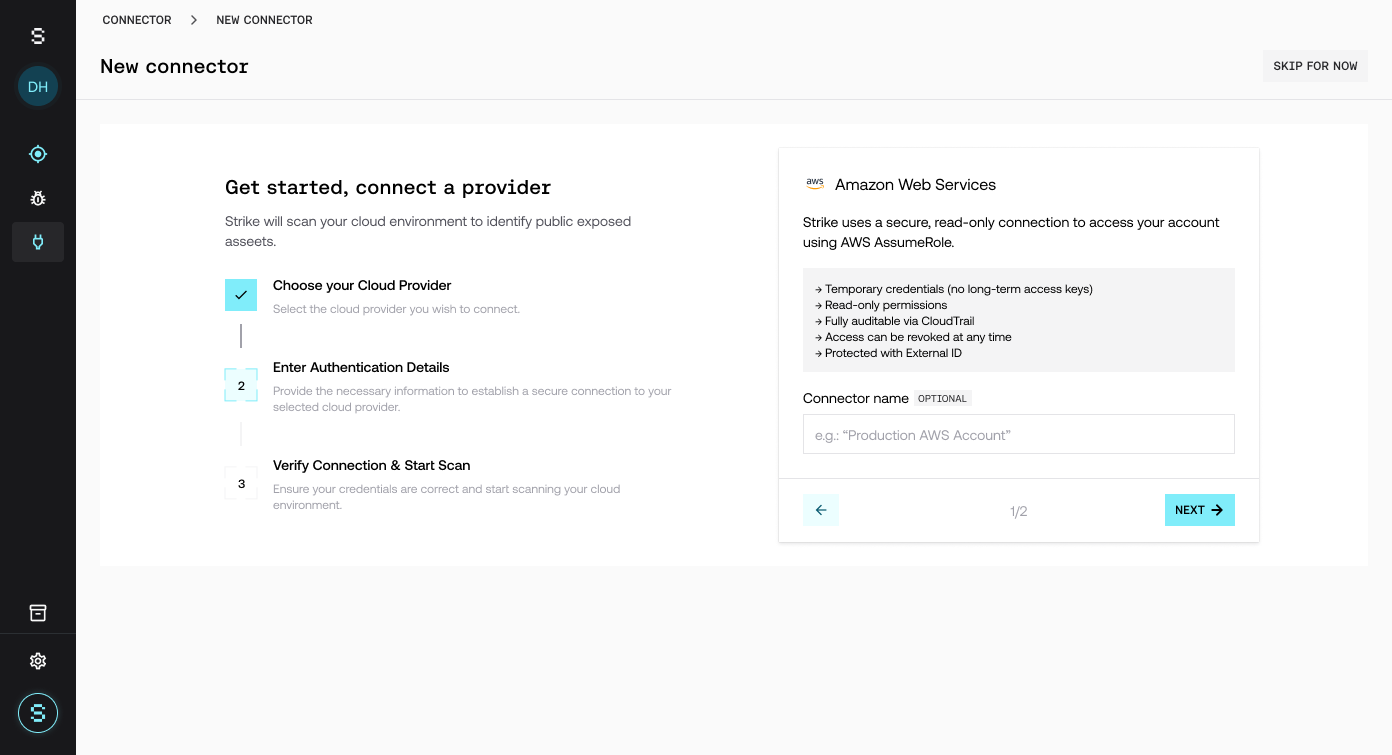
Give your connector a name. It will be visible and editable in the connector list. Strike connects to your AWS account through AWS AssumeRole with read-only access.
Step 3: Create the IAM role
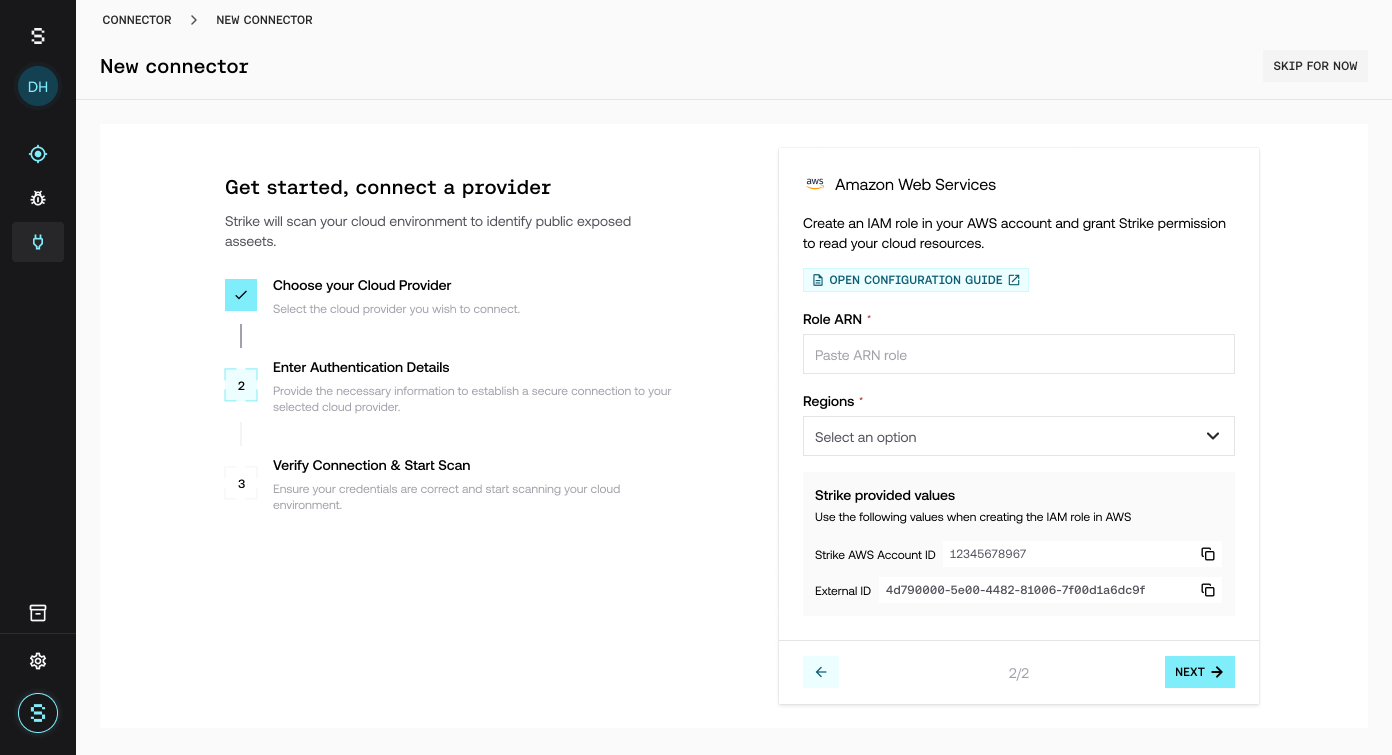
Open the Configuration Guide in Strike and follow these steps in AWS:
Go to AWS Console → IAM → Roles.
Click Create role.
Select AWS account → Another AWS account.
Enter the Strike AWS Account ID.
Turn on Require external ID and paste the value provided. Do not enable MFA for this role.
Step 4: Assign the permissions
Search for SecurityAudit and select the AWS managed policy.
Click Next.
Set the role name:
StrikeSecurity-SecurityAudit.Suggested description:
Read-only access for Strike.Click Create role.
Copy the Role ARN.
Important: the role name must start with StrikeSecurity to prevent the role from being assumed accidentally or without authorization.
Step 5: Add the role details in Strike
In Strike, enter:
Role ARN
Regions to scan
Click Next.
Verify the connection
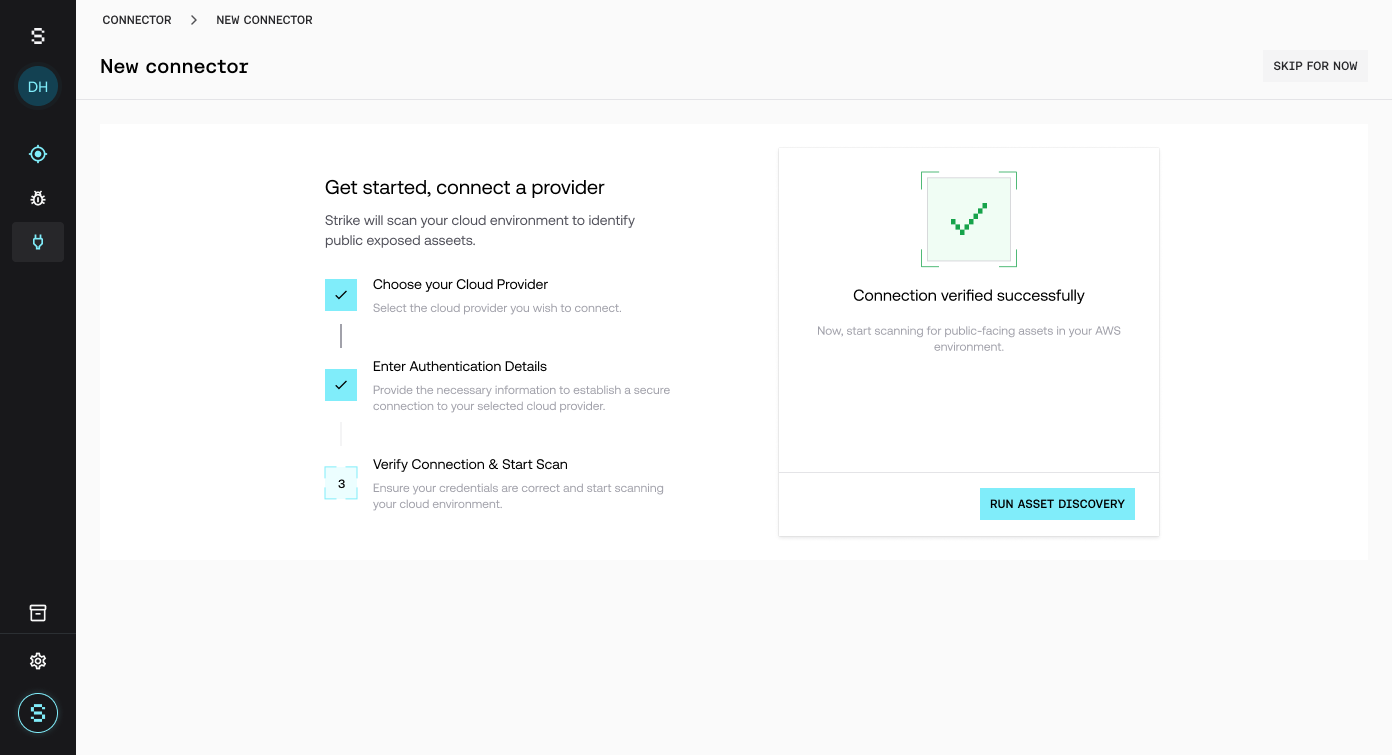
Click Test & Connect to verify access. If everything is correct, Strike confirms the connection and enables asset discovery.
Run asset discovery
After verification, click Run asset discovery to start scanning your environment for internet-exposed assets. Discovered assets appear in the Assets Inventory.
Managing connectors
You can manage connectors from the Connectors page in the sidebar.
Connector statuses: Connected, Pending setup, Failed and Inactive.
Actions: Test connection, Edit connector and Delete connector.
What Strike can do in your account
Strike uses read-only permissions to:
Discover cloud assets.
Identify exposed services.
Collect metadata for risk analysis.
Strike cannot modify or delete any cloud resource.
Frequently asked questions
Does Strike store my AWS credentials?
No. Strike uses temporary credentials through AssumeRole.
How do I revoke access?
You can deactivate the connector in Strike or delete the IAM role in AWS.
Can I connect multiple AWS accounts?
Yes. Each account is added as a separate connector.